ALL-SOC 3.0 · AI SIEM
An AI-native SIEM platform for intelligent security operations
ALL-SOC 3.0 unifies fragmented security tools into a single workflow — so analysts spend less time switching tools and more time responding effectively.
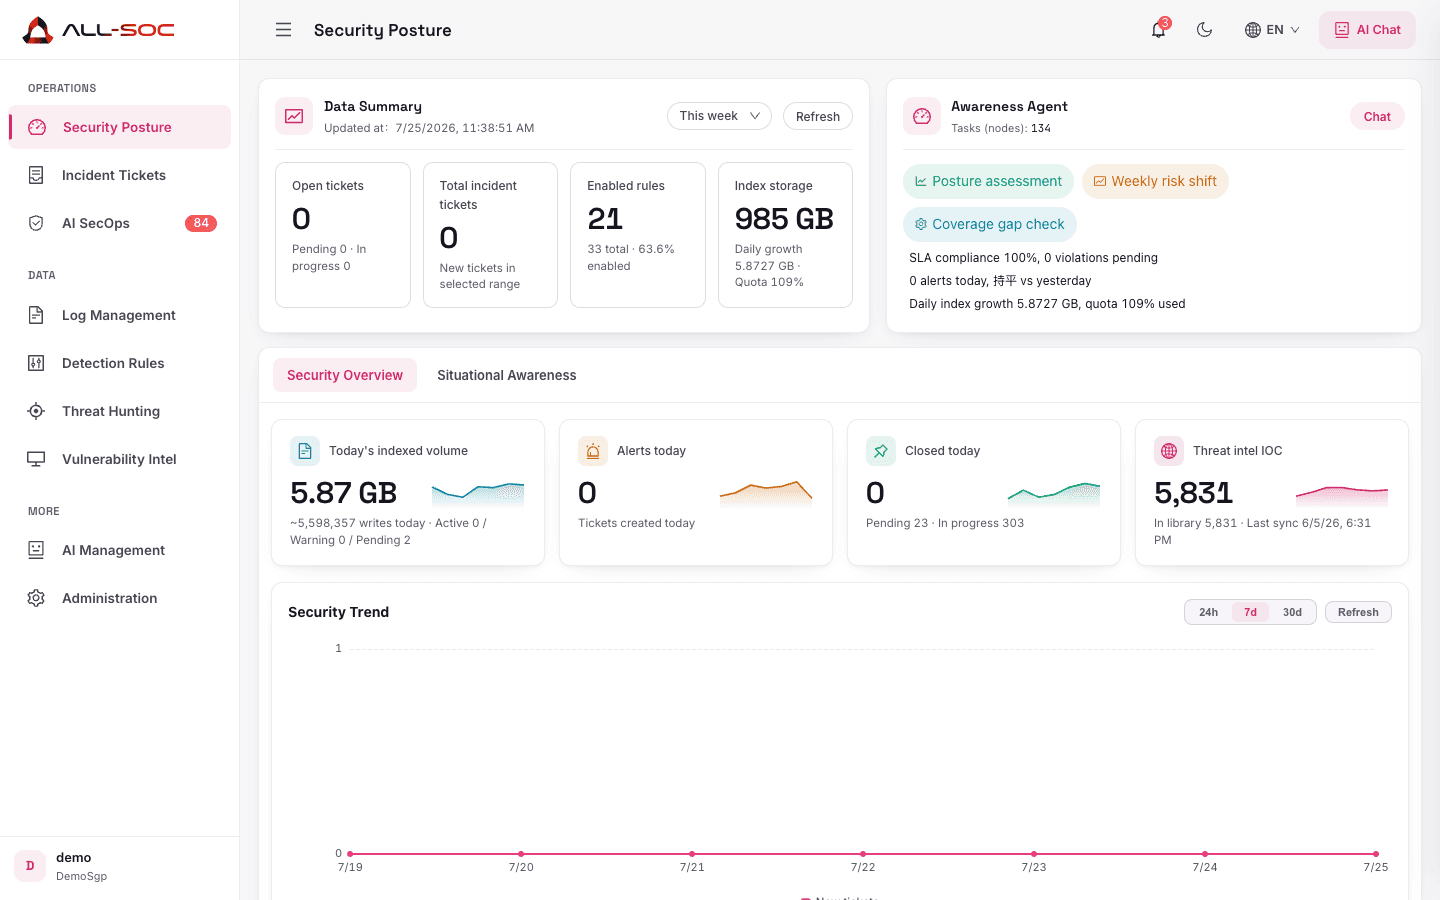
Operations Overview
The SOC command center. Real-time alert trends, open tickets, hunt tasks, and team workload — helping managers assess operational health and allocate resources.
- Real-time KPI dashboards
- Alert trends and categorization
- Team load and SLA overview
- Customizable views and filters
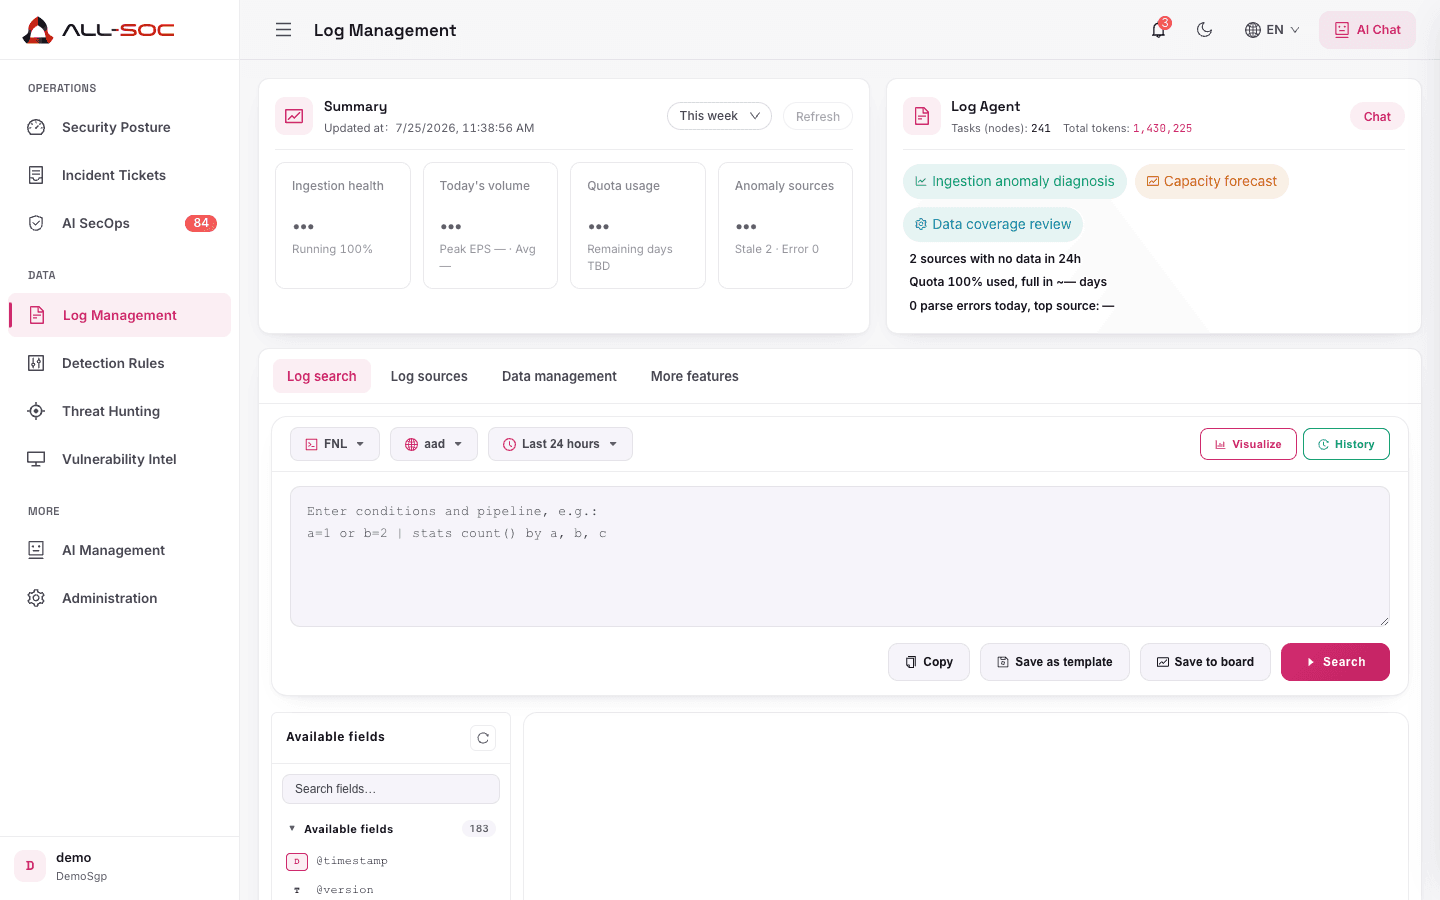
Log Management
Build a unified, searchable log foundation. Support for major log sources, field normalization, retention policies, and fast search — the data layer for detection and hunting.
- Multi-source connectors and agents
- Parsing rules and field mapping
- Retention and storage tiering
- Full-text search and saved queries
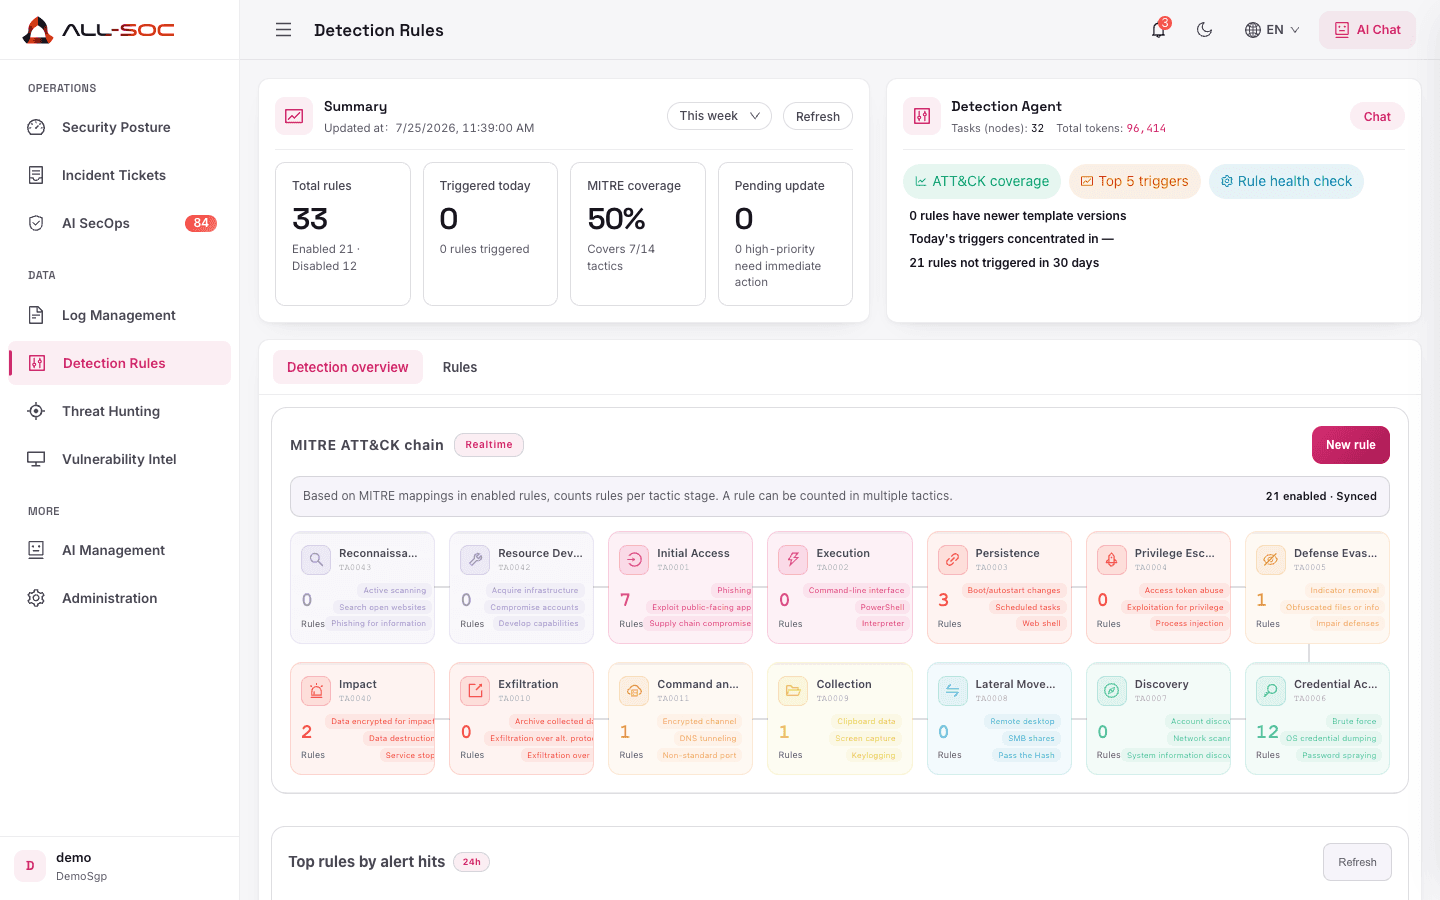
Detection Engine
From raw logs to investigatable events. Rule engine, correlation analysis, and baseline anomaly detection — auto-clustering noise into prioritized security alerts.
- Sigma/YARA-style rules
- Multi-event correlation
- False-positive feedback loop
- MITRE ATT&CK mapping
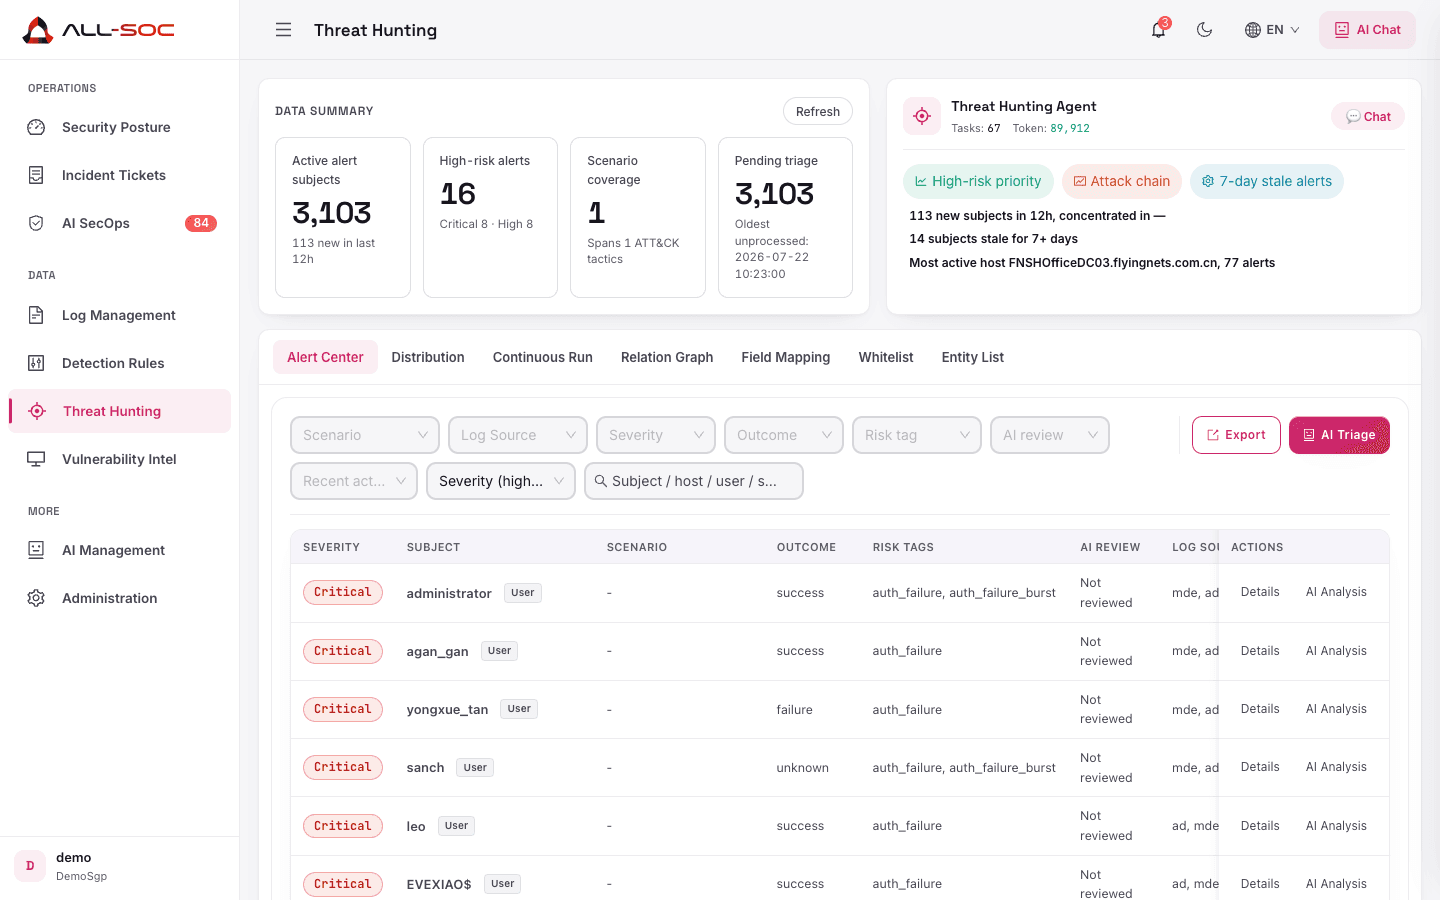
Threat Hunting
From passive response to proactive discovery. Pre-built playbooks covering common attack patterns, custom queries, and a seamless path from hunt findings to detection rules.
- Pre-built hunt playbook library
- Interactive query workbench
- Findings-to-rules workflow
- Hunt task collaboration
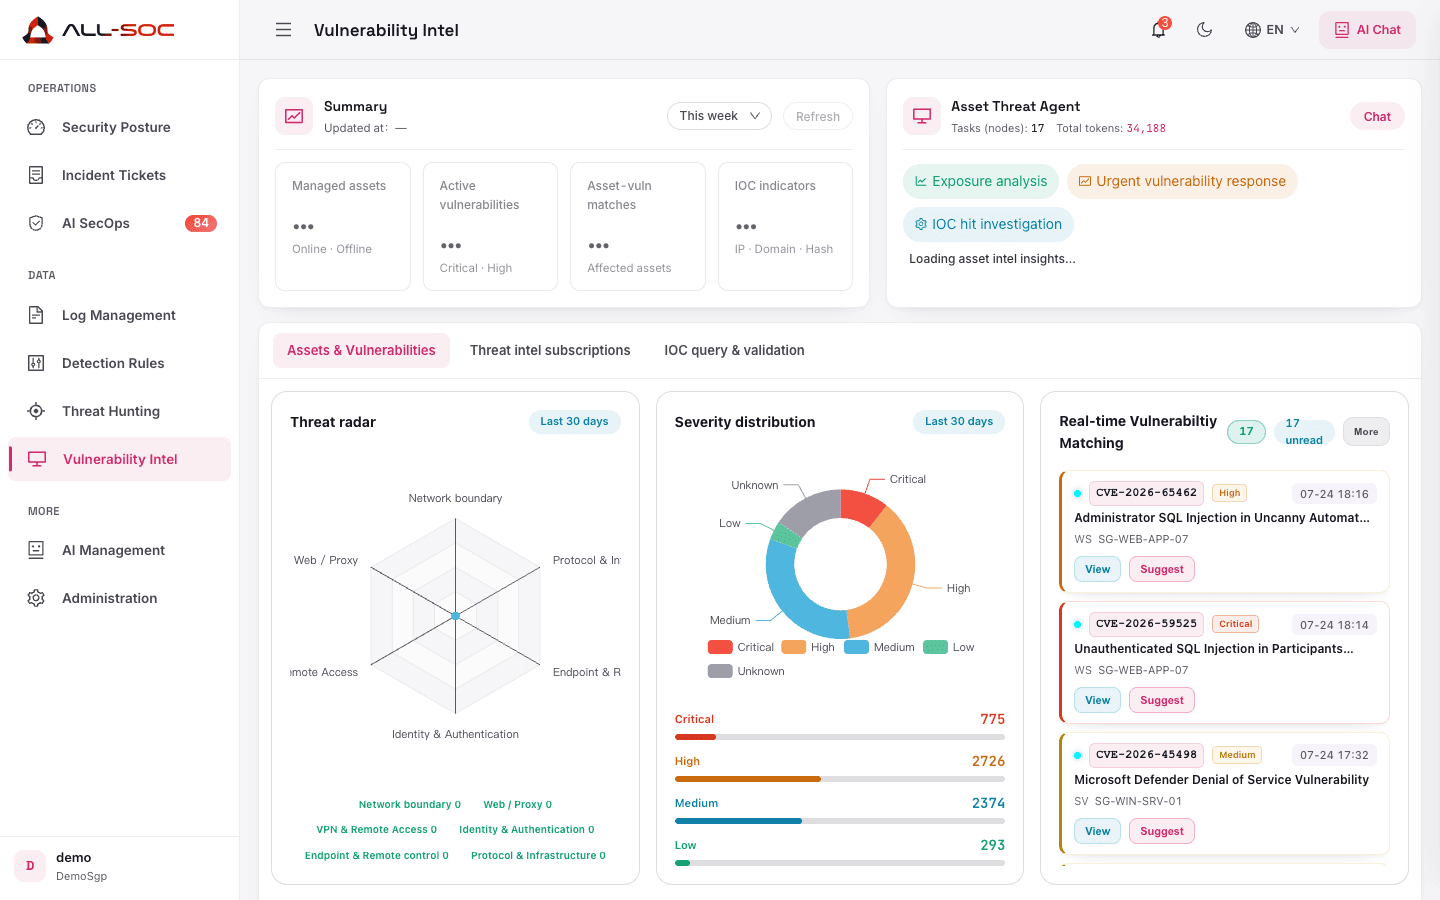
Asset Management
Context on every alert. Automated network asset discovery with CMDB sync, manual tagging for critical assets, linked to alerts, tickets, and investigation reports.
- Automated asset discovery
- CMDB/API sync
- Asset grouping and tags
- Risk scoring and exposure
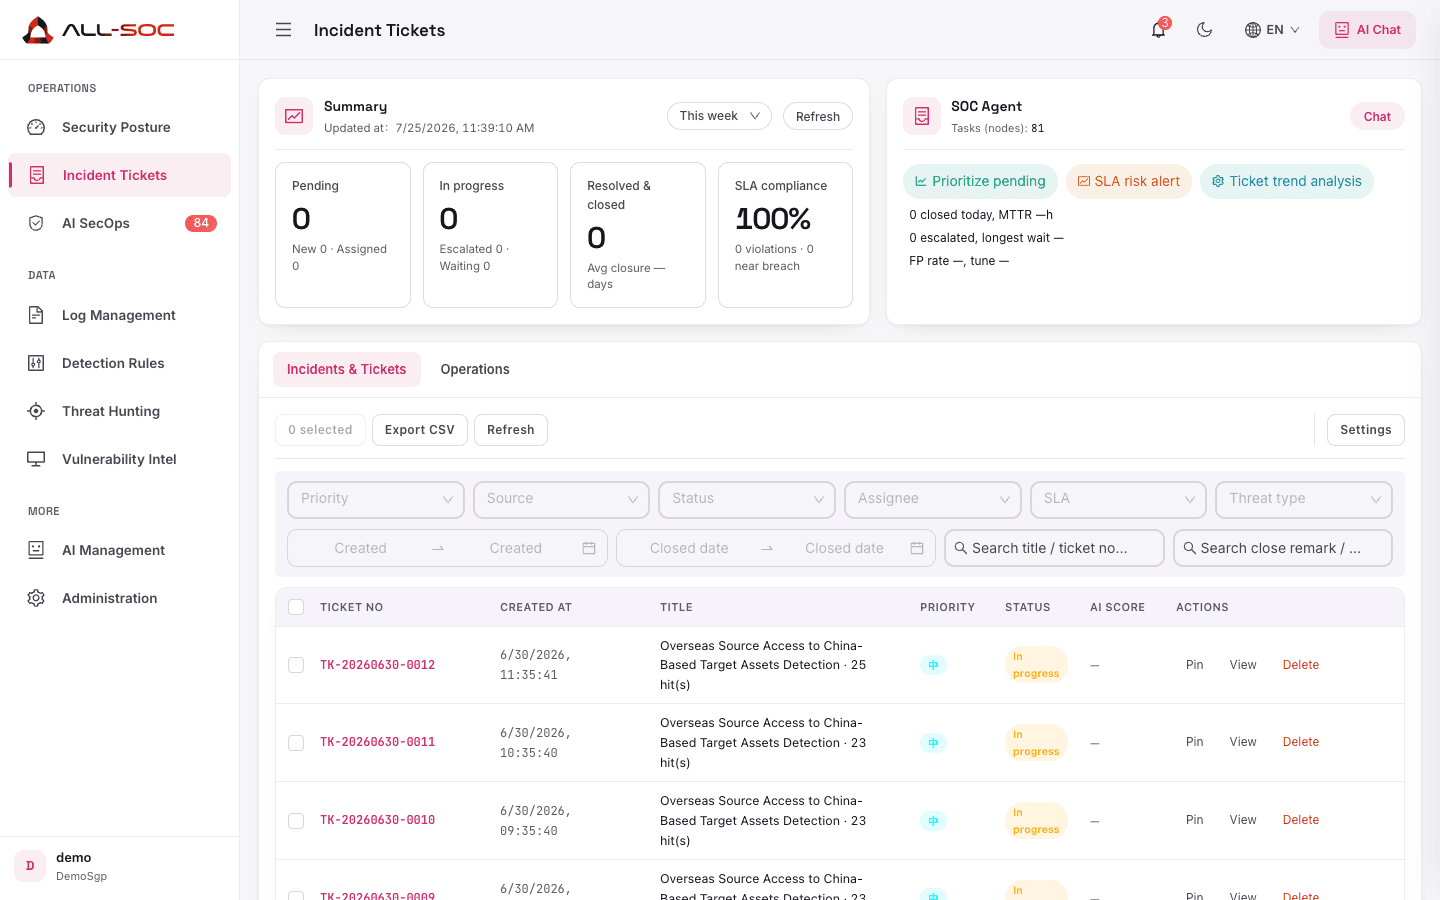
Ticket Response
Standardized incident handling. From alert triage and investigation notes to assignment, remediation, and post-incident review — fully traceable and auditable.
- Standard response playbooks
- SLA and escalation policies
- Collaboration timeline
- ITSM integration
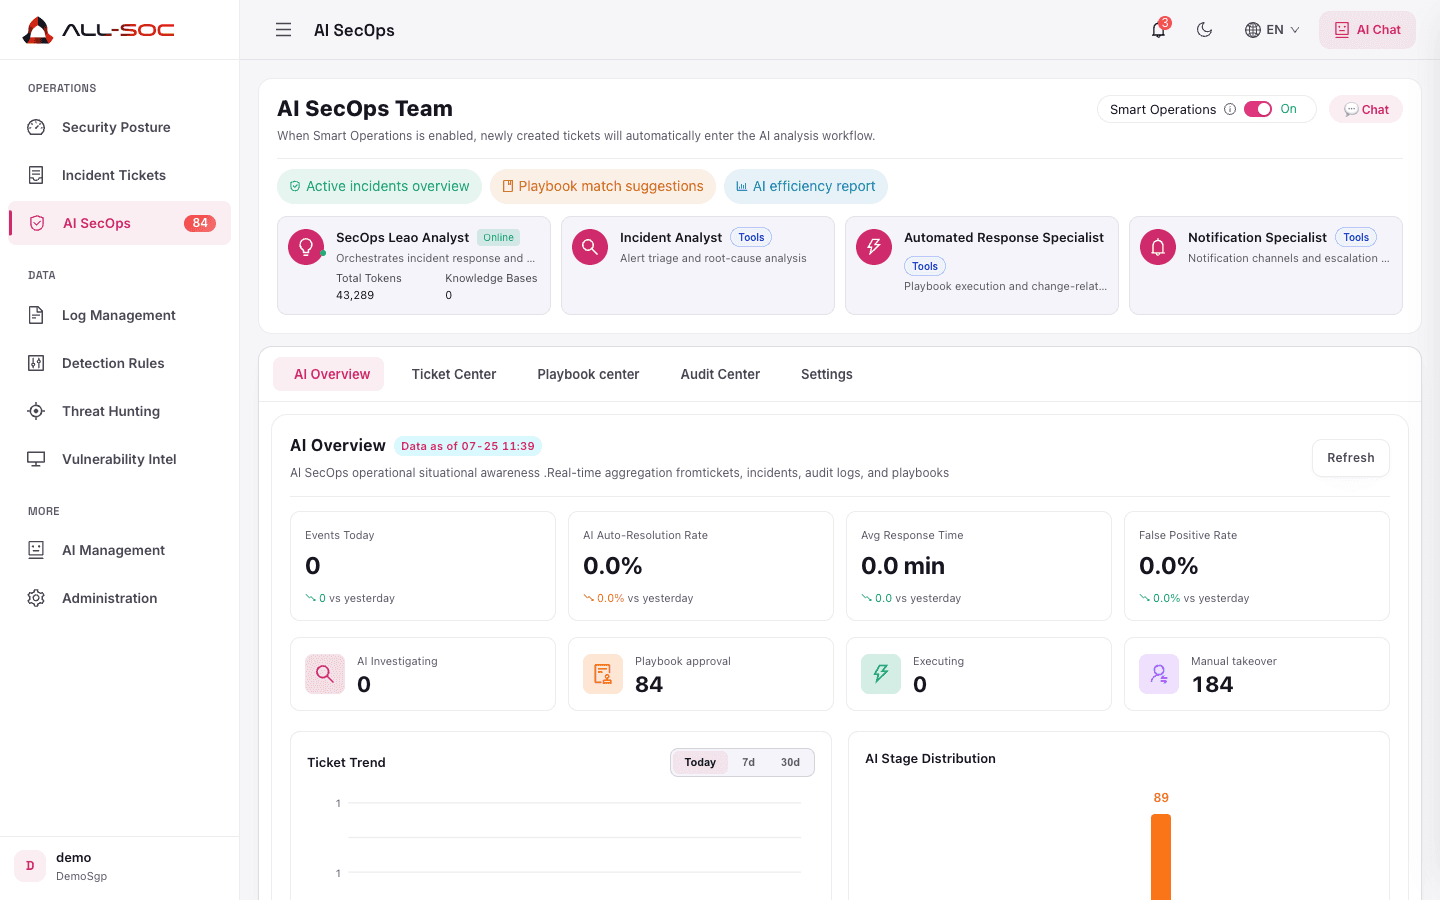
AI Operations Assistant
Conversational support for analysts. Context-aware investigation suggestions, log query help, and report summarization — augmenting decisions, not replacing judgment.
- Context-aware Q&A
- Investigation step suggestions
- Report summarization
- Auditable AI interaction log
Reports & Compliance
Auto-generated reports for leadership and auditors. Monthly ops reports, incident summaries, compliance mapping, and custom templates — less manual formatting.
- Auto-generated monthly reports
- Incident investigation reports
- Compliance framework mapping
- PDF/HTML export