Noise drowning real risk
False positives and low-value alerts consume analyst time while critical incidents stay buried.
AI Agent–driven enterprise SIEM
Alert noise, talent shortages, and fragmented tools slow response. ALL-SOC 3.0 is an AI Agent–driven SIEM that helps enterprises see clearly, find precisely, and respond faster—building an operable SOC.
Enterprise pain points
Alert overload, scarce talent, fragmented tools, and slow response—most organizations do not lack products; they lack an operable security system.
False positives and low-value alerts consume analyst time while critical incidents stay buried.
Dedicated SOC teams are expensive to build; nights and holidays often become coverage voids.
Logs, detection, tickets, and intel live in silos—investigations break and reviews stall.
From discovery to confirmation to response, manual workflows stretch into hours or days.
Threat landscape
Automated phishing, generative social engineering, adaptive malware, and AI-assisted reconnaissance lower the cost of attack and raise its speed. Enterprises need AI-native defense and operations.
Phishing, exploitation, and lateral movement are accelerated beyond human response tempo.
Signatures and fixed rules struggle against novel TTPs and long-dwell attack chains.
Identity, endpoints, cloud workloads, and apps intertwine—no single pane sees the full risk.
Why AI SIEM
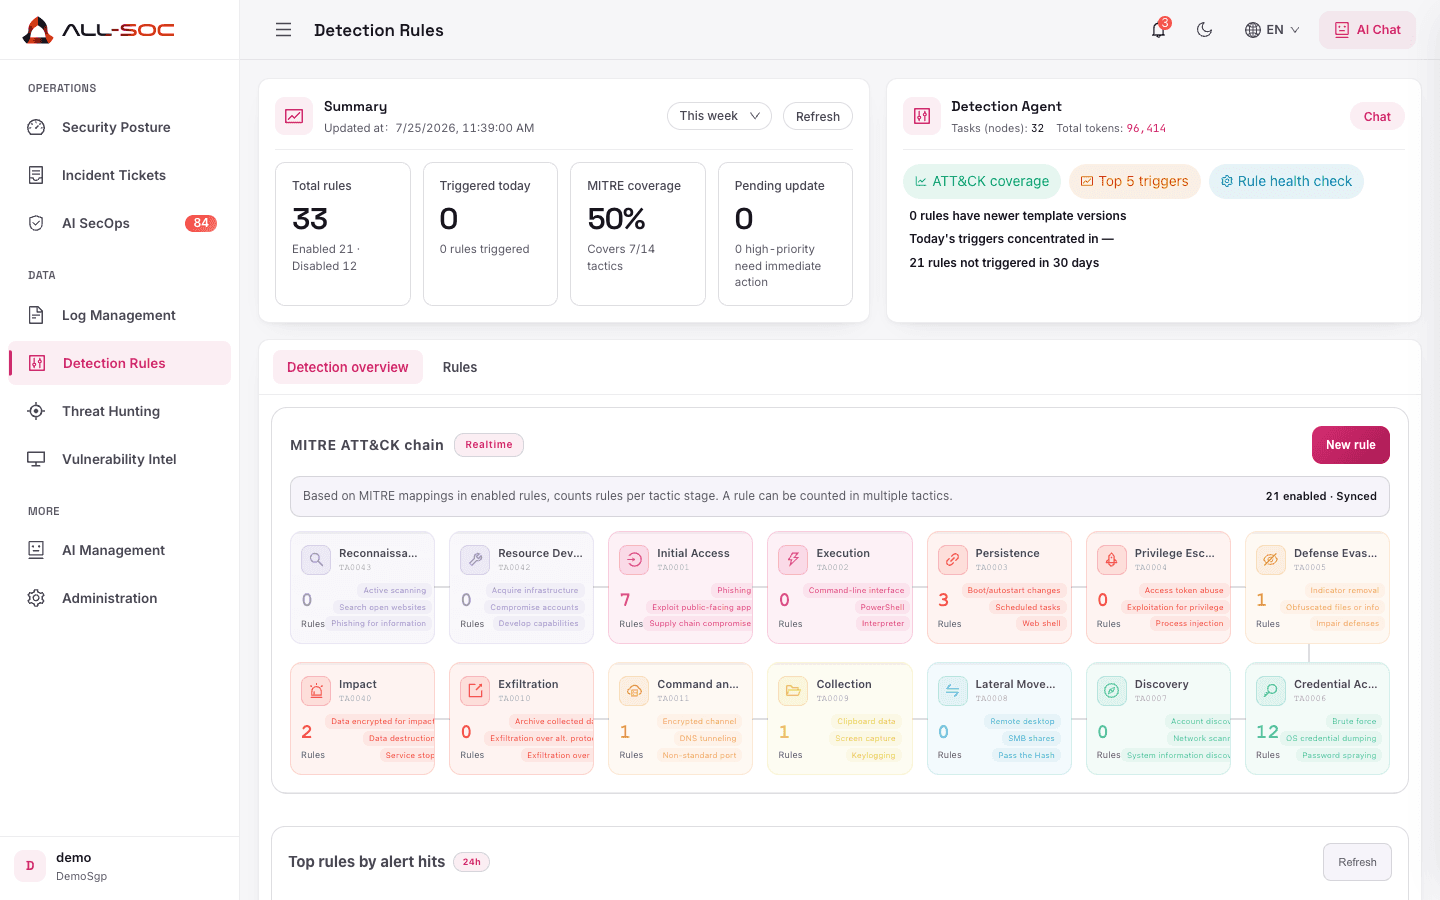
An AI SIEM is not another dashboard. It orchestrates collect, detect, hunt, respond, and report into a conversational, auditable, continuously improving operating system.
Unify logs, assets, alerts, incidents, and threat state into one operational picture.
Rules, correlation, UEBA, and AI reasoning work together to uncover known and unknown risk.
Analysis, approval, and Runbook execution form a closed loop that shortens MTTR.
Lower the SOC barrier so IT teams can run 24×7 operations with less specialist overhead.
ALL-SOC differentiators
ALL-SOC 3.0 builds a virtual security expert team with a 1+N AI Agent architecture—chat-native operations, traceable behavior, and progressive trust.
80%
Shorter MTTR
90%
Scenario coverage
10×
Signal quality
≥99%
Recognition accuracy
A Master Agent orchestrates domain specialists across detection, hunting, tickets, and reporting with cross-checks.
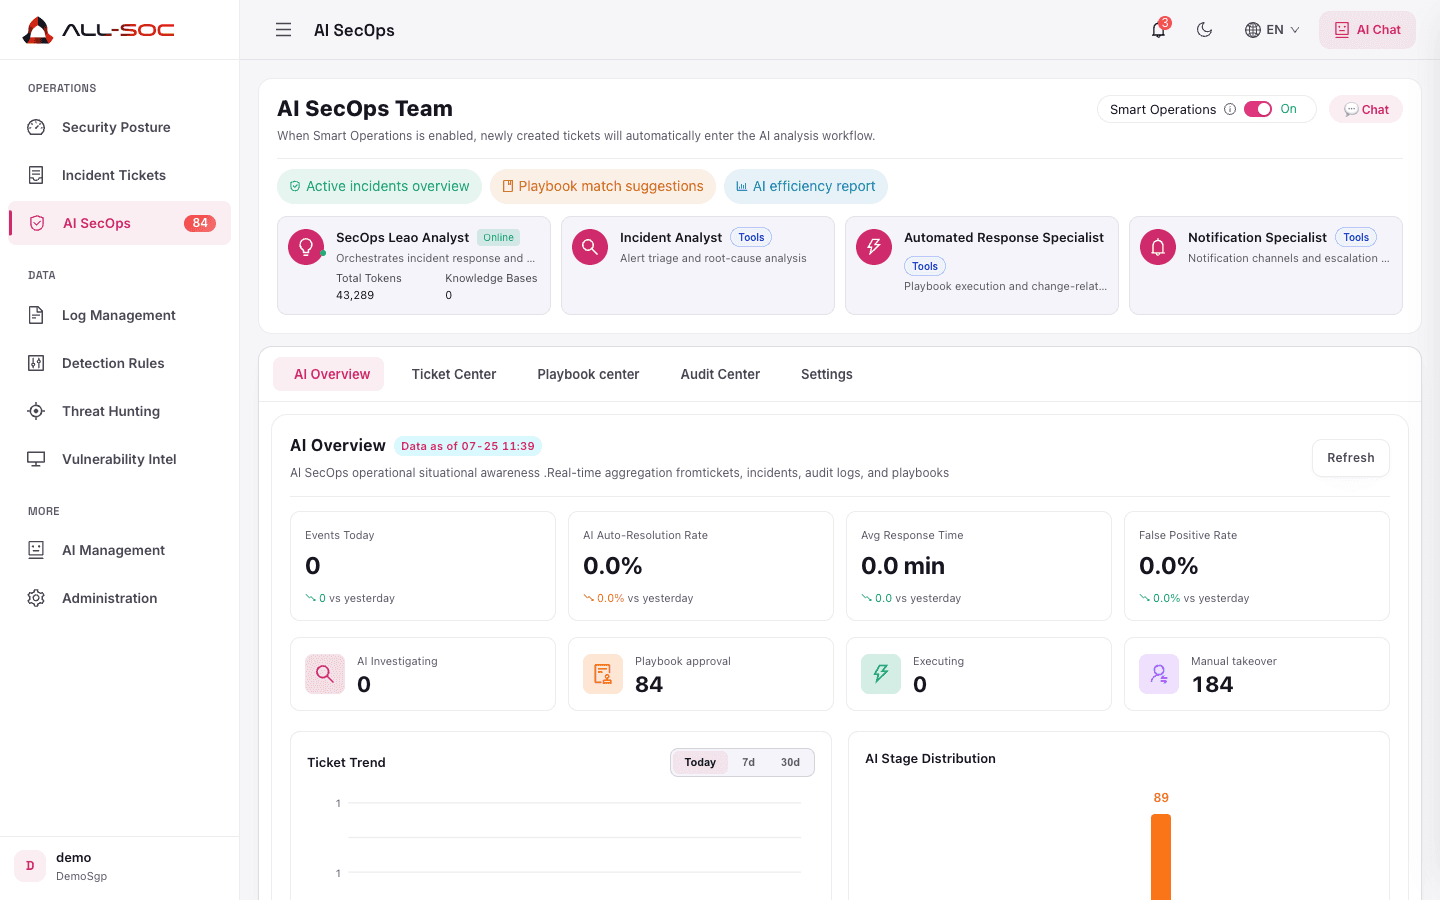
Search, investigate, and triage through conversation—learning cost can drop ~80% for everyday IT teams.
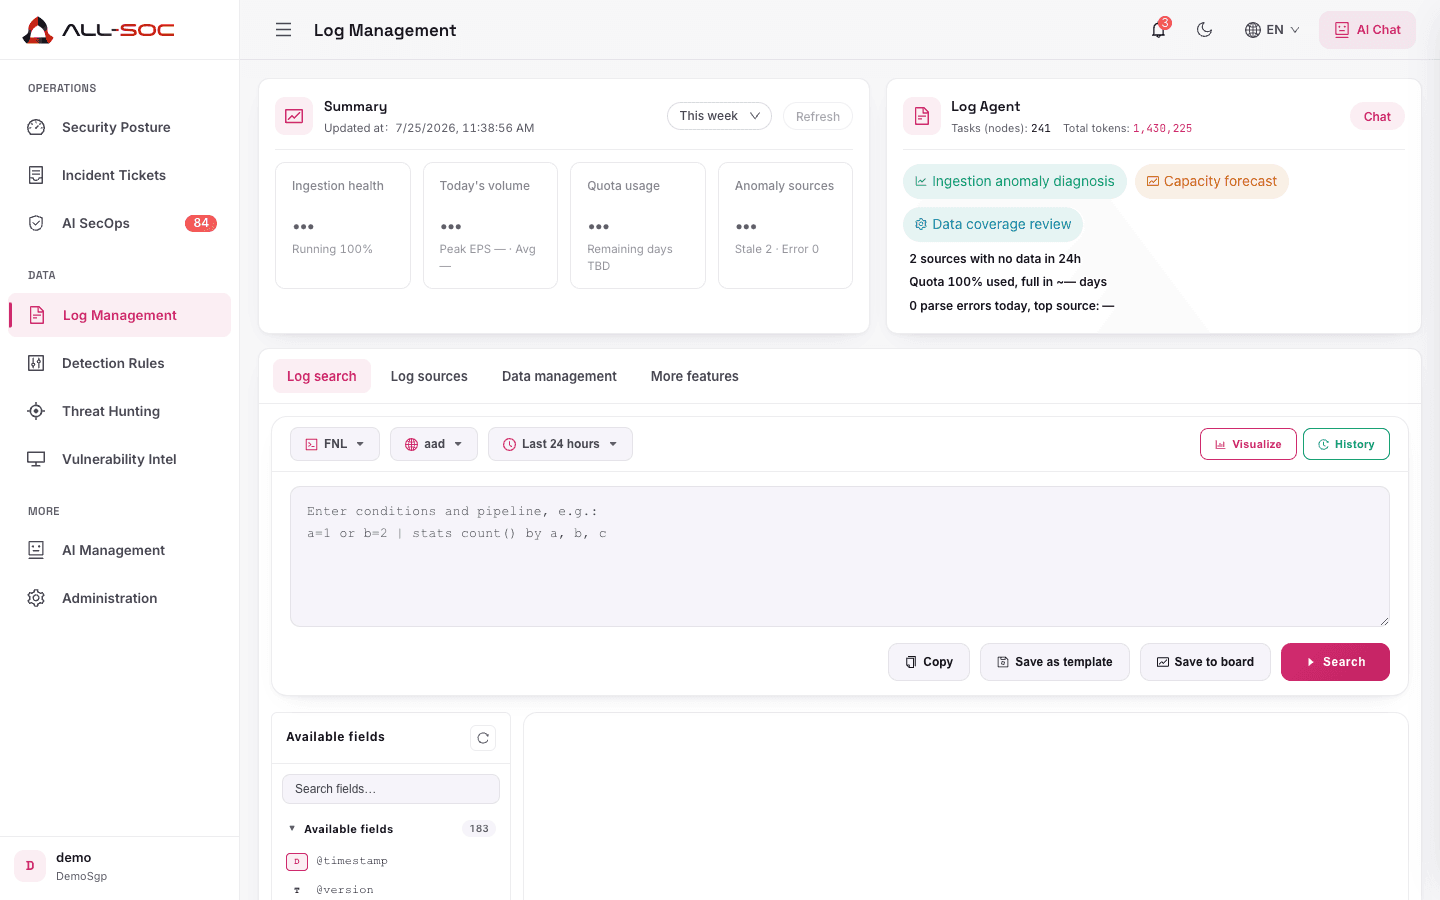
Semantic reasoning and attack-path reconstruction help teams move beyond wait-and-see detection.
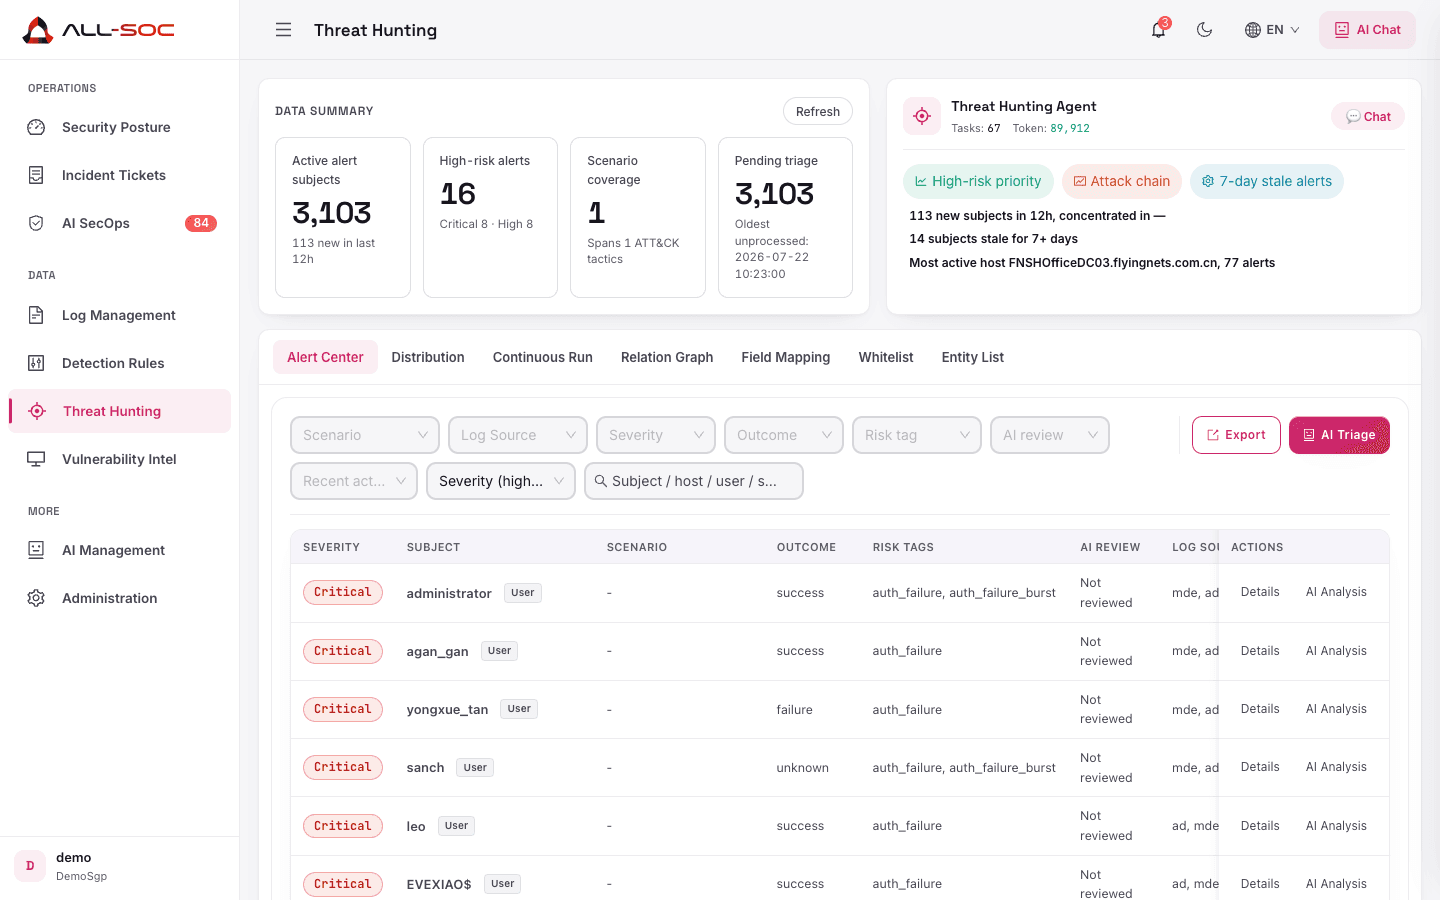
Chain-of-thought with HITL→HOTL→AUTO trust. High-risk steps contact humans per Runbook—intervenable and traceable human–AI collaboration, not a black box.